I think I figured it out. It only fails in older versions of Chrome. Firefox, and newer versions of Chrome, still have the /users/ link, but instead of going to a 404 page on click, it pops up a user summary widget.
So… I think that “bug” can safely be ignored.
This is probably exactly the sort of thing which motivated the Discourse devs to reject everything but the most recent browsers. 99% of the site works fine, but one tiny part doesn’t, so the browser goes on the “unsupported” list. Or at least, that’s how I imagine that list was made.
Yep, that’s what I understand too.
With that said, that’s a really weird bug, I don’t see how the browser could generate an incorrect URL even with an old Javascript engine??
Questions for the admin:
Are there google ads on this site? How is google adsense used?
The privacy policy used to say:
" Visitor access logs are never kept for more than 28 days. Under normal circumstances, access logs are discarded after 1 hour."
It no longer says this. Has the log policy changed? If so, what is the current policy?
When typing replies, is the “draft” content stored on the user’s machine or on the server? It appears to be server side, and presumably transmitted letter by letter. I wonder if every keystroke is logged, regardless of whether it was “saved.”
Also there appears to be a DOMRect canvas object according to CanvasBlocker. I don’t know what it does. I notice no changes with it blocked.
Actually I liked the edit diff. When I edit my posts, it’s usually not because I regret having written something, but to make something more understandable or add more details. Think before you post. Sadly some people abuse the edit and delete functions. But you can’t unsay and take back something, you can only ask for forgiveness.
So where’s the problem? Just because some features can be abused for fingerprinting doesn’t mean they are useless. This website is very dynamic and needs to know where the user is looking on the page and how they interact with it.
Not at the moment. The old forum always did. Depending on how many banner spaces are filled with direct ads from flashlight vendors I might re-enable Adsense here at times. Adsense is used on millions of websites to show ads, and it involves adding a short block of code to the webpage which in turns calls a script on Google’s server that places the actual ad that Google’s customers pay for, and Google pays a small percentage of that price to the website that displays the ad.
Has the log policy changed? If so, what is the current policy?
I temporarily removed the log retention period number for the simple reason that I don’t know yet, since the server architecture is completely new and largely unchanged from the defaults. This forum is built from a sort of “recipe” script that pulls in open source components from different open source software projects and then applies a default set of configurations and then runs them in containers, so I haven’t manually configured anything relating to logging. I normally spend little to no time perusing the logs, as I have absolutely no interest or time to waste on that, and I do not share or sell or earn money from the logs. The logs are only useful for me to determine if a user is trying to do something nefarious or to diagnose a technical issue.
Correct. That’s how it allows for starting a reply on one device and then finishing it on another device.
It does not. It saves a snapshot of the draft message every few seconds, and the next snapshot replaces the previous one. You can test this by starting a new reply and quickly typing some random keys with one hand and then quickly closing the browser tab with the other hand. Then check your Drafts and you’ll find that it either didn’t have time to save the draft at all or it will show a previous state from before you stopped typing.
Me neither. Looks like it’s for placing stuff on the page:
I’m not a programmer or web developer myself, so I use software that others create and maintain. But one of the main reasons why I insist on only running open source software from the ground up on this server (and also my personal computers) is that it’s much less likely that the developers of an open source project would do anything stupid like adding privacy-violating phone-home data-siphoning functionality. And if they were to add it then there are tons of eyes on the code and there would quickly be public outcry and and mass exodus of users and developers to a different open source offering. You’ve all probably noticed that I myself am very private and I maintain a very low online profile, so I respect and support the privacy of users here as well.
This is the latest rabbit hole I’ve gone down. I recently ordered a new Ryzen cpu, motherboard, and ram to upgrade my 10+ year old PC, mainly because 16GB ram isn’t enough for me anymore, and while these parts were in transit to me, only then did I start reading about the platform security processor (psp) in the AMD chips, and Intel IME, and how these devices may compromise a system. The psp is in 2013 or newer AMD cpus and the IME has been in Intel chips since ~2008. Then I read a bunch of stuff related to security, fundamental problems with X86, DMA and shoddy IOMMU implementations, rootkits, exploits and vulnerabilities, about binary blobs and proprietary hardware and firmware, and what options exist for open hardware and firmware. Qubes OS, the FSF and GNU, blobless Linux, open NICs, IBM Power9 and the Talos II, Coreboot, Dasharo, me_cleaner, etc.
I am curious what hardware, firmware, and OS you’ve chosen and just how far you gone to avoid blobs and omnipotent co-processors.
Hmm yep, tons of things to take into account there.
Personally I draw the line between firmware/drivers on one side, and the rest of the OS and user-facing programs on the other. I definitely don’t like the proprietary blobs and co-processors either, but it doesn’t seem feasible for me to accomplish normal computing tasks without them. It’s always worth testing one of these FSF-approved Linux distros to see if your hardware happens to be favorable for running without proprietary firmware blobs; some are “live” systems that can be run from a USB stick to test it before committing to the installation. But there are usually huge compromises to running those 100% libre distros on most hardware. I’m personally not too concerned about the potential risk of targeted surveillance against me. And I think there would be less motivation to spy on users in the case of a hardware vendor with a revenue model based on expensive physical products vs. an operating system vendor like Microsoft that is trying to transition to a Software-as-a-Service business model where the end user is the principal product. I would love to be able to run Coreboot, but unfortunately it’s not supported on most motherboards. I did buy a laptop from a vendor that specializes in Linux-compatible hardware with Coreboot pre-installed, but in my case the laptop was a lemon and I had to send it back for a refund after a failed attempt to repair the critical physical defect. I can PM you the name of the company if you want, I wouldn’t recommend them based on my experience, but I don’t think my experience would be the norm either, and they were an honest and responsive company to deal with.
A lot of potential risks and vulnerabilities at the most fundamental levels of computing seem to be more theoretical in nature, whereas we all have probably experienced in real life the very real privacy and security issues than can arise with Windows. I wouldn’t say that Windows can’t be made safe and private, but it sure requires a lot of work and vigilance to keep it that way. So in my case and probably in many others, I think the biggest gain in real-life privacy and security with the fewest tradeoffs is to replace Windows with Linux. I personally stick with the mainstream Linux distributions for the base of my system, as I don’t want to be stuck with an unsupported OS if the only developer disappears. I run a heavily customized openSUSE Tumbleweed system on a machine where I need newer software, and a customized installation of Debian Stable on other systems that I don’t want to change frequently. There are spinoff distributions of both of those OSes that still depend on the parent project but offer a subjectively better set of defaults and a faster installation method.
I was not logged in for a couple weeks, (due to a recent hernia injury & life’s tornadoes ) but came back a a complete different looking BLF, (with the password reset) im still scratching my brain on to what happened lol.
Hey there @DBSAR , great to see you here! Yep, this has been in planning since last October, this post explains some of the reasons why it was necessary: https://budgetlightforum.com/t/updated-2023-02-10-migration-complete/71360#original-post-5
I know it’s quite different especially for our long-time users. It wasn’t a decision I took lightly, but it was necessary, and I made sure it would meet the specific needs of the BLF community. I’m happy to receive feedback and specific suggestions to improve, and questions are welcome too.
Things are still a little bumpy around here after the platform change, but the issues are quickly being worked out. So things may continue to change for a while, but it’ll be for the better.
Sounds like things have been rough. I hope the wind will calm down soon!
I’ve had this issue twice now, i had no new posts as of yesterday and @DBSAR 's post just showed up now (despite being a day ago) and another 14 day old post also showed up only yesterday.
That’s just because it was originally in the “BLF Site Issues” category description thread, which I didn’t realize was open to comments, and it’s not very visible there. So I moved it to this thread so more people would have a chance to say Hi.
That also might have been me testing moving another post from one thread to another.
So far I’ve personally been really impressed with how Discourse has helped me keep track of the threads I’ve been participating in.
Thanks for the great work & dedication SB! It will take some getting used to, especially how the topic pages work. The new site lay-out looks interesting, Like a new paint job!
Thanks for saying so @DBSAR. I really hope you like it. It’s actually a completely different forum platform through and through, so it has a lot of new features and probably a thing or two that still needs to be refined a bit.
I hope things calm down a bit for you there, and we all look forward to seeing you around here!
Thats interesting.
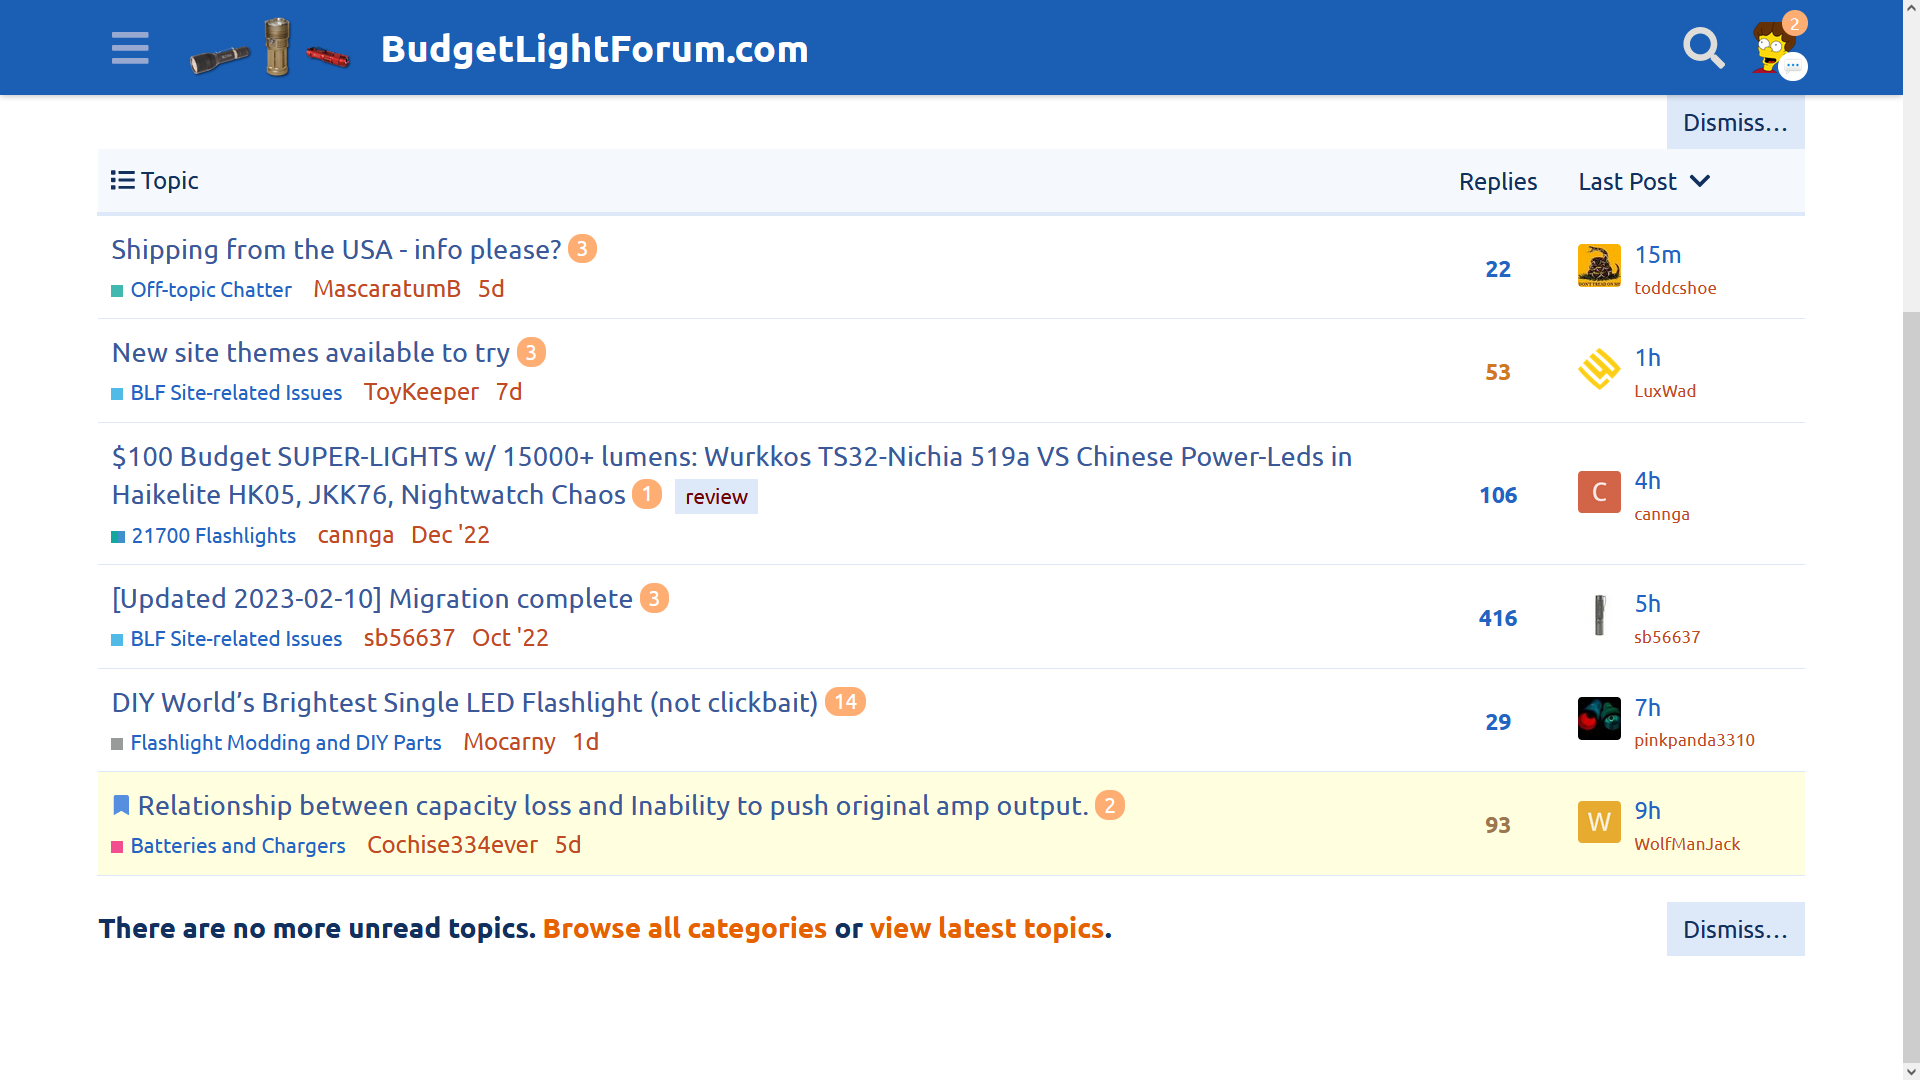
I don’t mind it, but perhaps an explanation if possible, can you add a bookmarked label on highlighted threads so people know what the yellow means?
Perhaps something like [Bookmarked] or [Bookmarked post in thread] maybe after the 5d in my example?

 ) but came back a a complete different looking BLF, (with the password reset) im still scratching my brain on to what happened lol.